Permissions (Part 1)
LPIC-1LINUX
TL;DR
File - r - cat
File - w - modify the contents of the file (vi)
File - x - executes
Directory - r - ls
Directory - w - create/delete/rename files (it also needs "x" permission)
Directory - x - cd
r-x usually together - Read Only directory
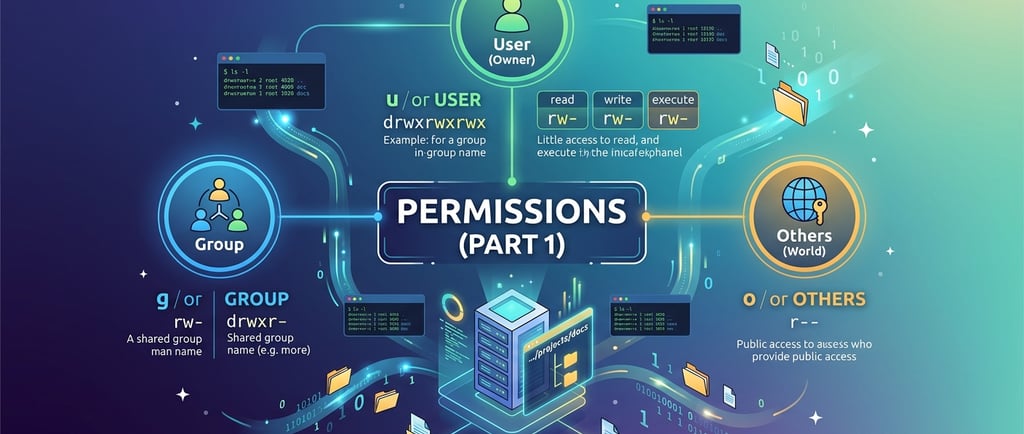
The rule: the kernel checks only one category, in this order: are you the owner? Use the owner bits. If not, are you in the file's group? Use the group bits. Otherwise use the other bits. It stops at the first match and never falls through to a more generous category.
------------------------------------------
1. Files vs. Directories cheatsheet
The primary difference lies in whether you are interacting with the data inside a file or the list of filenames inside a folder.
Permission For a File For a Directory
r (Read) You can view the file's contents (e.g., cat, less). You can list the files inside (e.g., ls).
w (Write) You can modify the file's content or truncate it. You can create, delete, or rename files inside.*
x (Execute) You can run the file as a program or script. You can "enter" the directory (e.g., cd) or access metadata.
The Execute Bit for Directories
The x bit is the most critical for directories. Without it, you cannot access anything inside, even if you have read permissions.
(*) In technical documentation, it is often listed Write, as the permission that allows modification of the directory's entry list (creating/deleting), but in reality when you want to delete a file, you also need the Execute (x) permission for the directory (to also enter the directory). To delete a file, your system must perform two distinct actions:
Access the directory
Delete the file
2. Numeric (Octal) Representation
Linux permissions can be expressed with three digits (e.g., 755 or 644). Each digit represents a sum of values for Owner, Group, and Others.
Read (r) = 4
Write (w) = 2
Execute (x) = 1
Common Combinations:
7 (4+2+1): Full access (rwx).
6 (4+2+0): Read and write (rw-).
5 (4+0+1): Read and execute (r-x).
4 (4+0+0): Read only (r--).
3. Practical Scenarios
Whether you can delete a file or not
A common point of confusion is file deletion. Even if a file is marked 000 (no permissions at all), a user can still delete it if they have write (w) and execute (x) permissions on the parent directory.
The "List but No Access" Scenario
If you have r on a directory but not x:
You can run ls and see filenames.
You cannot see file sizes, types, or owners (you’ll see question marks).
You cannot cd into it or open any files within it.
Permission Combinations in Practice
Combination Practical Ability
--x (1) You can access a file if you already know its exact name, but you can't see what else is in there.
r-x (5) The standard "Read Only" directory. You can ls and cd, but you can't touch the files.
-wx (3) You can create or delete files if you know the names, but you can't list (ls) them.
rw- (6) You can see the names (ls), but you cannot cd, delete, or create anything.
4. Quick Command Reference
To view permissions, use ls -l. The output string (e.g., -rwxr-xr--) breaks down as:
First char: Type (- for file, d for directory).
Chars 2-4: User/Owner permissions.
Chars 5-7: Group permissions.
Chars 8-10: Others permissions.
To change them, use chmod:
Symbolic: chmod u+x file.sh (adds execute to user).
Absolute: chmod 644 file.txt (sets to rw-r--r--).
Practice exercises
Do these as your normal user in your system, in a directory you create called "testdir". Predict the result before you run each command.
Exercise 1: owner permissions
$ echo "hello" > file1
$ ls -l file1 # you are the owner
$ chmod 000 file1
$ cat file1 # what happens?
$ chmod 400 file1
$ cat file1 # now?
$ echo "more" >> file1 # and writing?
Exercise 2: execute permission
$ echo 'echo "I ran"' > script.sh
$ ./script.sh # fails: no x
$ chmod u+x script.sh
$ ./script.sh # works
Exercise 3: owner vs. others
$ sudo bash -c 'echo "root file" > rootfile'
$ sudo chmod 644 rootfile
$ cat rootfile # readable? you are "others" here
$ echo "x" >> rootfile # writable?
$ sudo chmod 600 rootfile
$ cat rootfile # now?
Here you're not the owner, so the "others" digits are the ones that apply to you.
Exercise 4: directories
$ mkdir dir1
$ touch dir1/a
$ chmod 600 dir1 # r and w but no x
$ ls dir1 # what do you see?
$ cat dir1/a # can you open the file?
$ chmod 100 dir1 # x only
$ ls dir1 # now?
$ cat dir1/a # now?
For special permissions, go to Part 2.
Contact
hello@unixtips.eu
© 2025. All rights reserved.